
Good fit
One use case has someone accountable for the outcome, a baseline the business already measures, and users who can judge whether the result improves.
Controls and audit trail
BluePi turns governance requirements into accountable owners, platform controls, review paths, and an audit trail inside delivery.
For governance that must change daily behavior
BluePi connects governance to the systems, data products, reports, models, and workflows where risk and trust are created. The scope can include metadata, quality, access, privacy, lineage, retention, and day-to-day ownership.
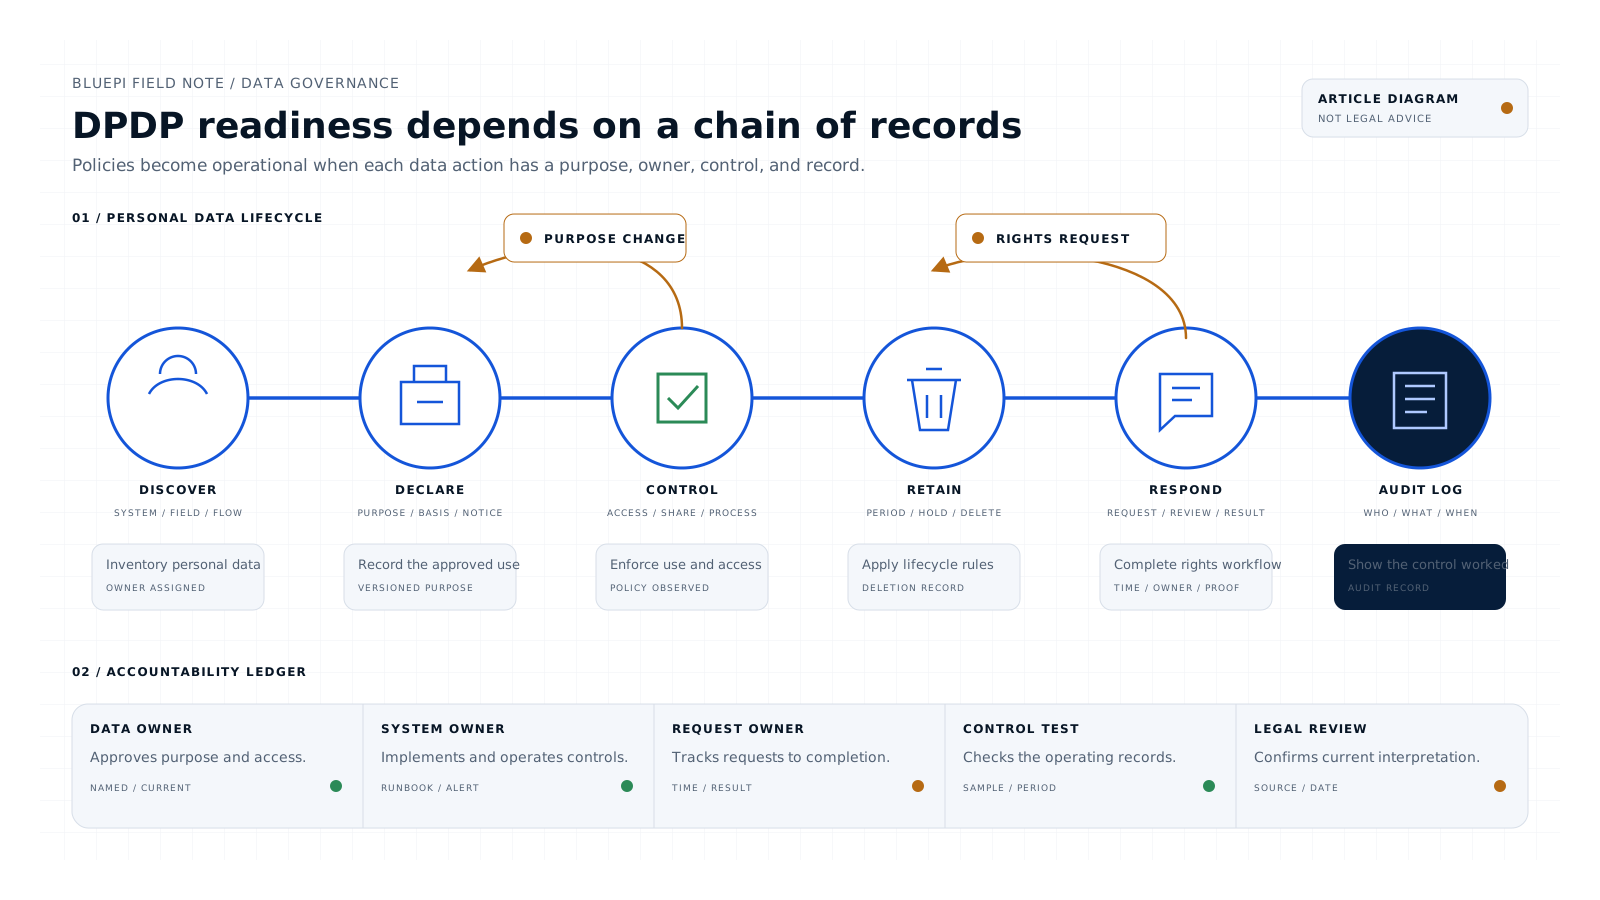
For readiness under India’s Digital Personal Data Protection Act (DPDP), BluePi traces personal data through purpose, collection, access, sharing, retention, deletion, and rights workflows. Technical and process controls are linked to records that owners can review.
When this is the right starting point
Good fit
One use case has someone accountable for the outcome, a baseline the business already measures, and users who can judge whether the result improves.
Poor fit
The request is capacity-only staffing, an unowned demonstration, or a broad transformation without a first decision and finish condition.
What you receive
01
The first scope covers data that supports material decisions, regulated processing, customer workflows, or AI systems.
02
Teams record meaning, source, allowed use, retention, ownership, access, quality, lineage, incidents, and exceptions.
03
Quality controls define the expected grain, completeness, validity, consistency, freshness, and reconciliation for important data. Scorecards, ownership, alerts, exception handling, and recorded check results keep those controls active after release.
04
Training data, retrieval sources, evaluation sets, human review, and output retention use the same ownership and audit model as the underlying data platform.
Ownership, quality, access, privacy, and lineage requirements turned into deployed controls and reviewable audit records, running with the system rather than as a side document.
Yes. BluePi has published readiness work across consent, data discovery, data principal rights, retention, and the overall DPDP compliance operating model.
We will look at who owns the decision, the current baseline, the data involved, what the system must include, and the route to go-live.
Discuss a use case